AI-Driven Cyberattacks: How ARTEX Hit South Korean Banks

AI-Driven Cyberattacks: How ARTEX Hit South Korean Banks
AI-driven cyberattacks are no longer a “future problem”. In late September and early October 2026, a series of breaches hit South Korean banks and other lenders, and security researchers say an AI-powered hacking tool helped the attacker work faster. The tool is called ARTEX, and the story behind it shows how both attackers and defenders are changing the way they work.
In this post, I explain what happened in plain words, how the attack worked, what we still do not know, and what you can do to protect yourself or your business.
Quick Answer: What Happened?
- Who was hit: At least seven South Korean financial companies reported leaked customer, company or staff data.
- What was used: A Chinese-developed, open-source tool called ARTEX, plus several AI models, plus normal hacking methods.
- Who did it: Unknown. CrowdStrike says the person is likely Chinese-speaking and driven by money, but this is a “moderate confidence” view, not proof.
- Why it matters: The attacker moved faster and hit many targets in a short time because AI did much of the repeat work.
What Are AI-Driven Cyberattacks?
AI-driven cyberattacks are attacks where a hacker uses artificial intelligence to do part of the job. This can mean scanning for weak spots, writing code, planning the next step, or checking if a break-in worked.
Think of it like cooking. A hacker used to chop every vegetable by hand. Now they have a kitchen assistant that chops, stirs and tastes, while they just say “make dinner”. The recipe is the same. The speed is not.
What Happened to South Korean Financial Institutions?
Starting in late September 2026, several South Korean financial institutions reported that customer data had leaked. News reports say about 25,000 customers were affected at Shinhan Bank and about 40,000 at Yegaram Savings Bank. KB Kookmin Bank and Hana Bank also reported smaller incidents. Reports say the leaked details included things like names, phone numbers, income and loan limits.
The government responded quickly. South Korea’s Financial Services Commission held an emergency meeting, and regulators asked around 500 financial firms to check their systems. The president also asked for a full investigation.
Officials say direct money theft looks unlikely. But leaked personal data is still valuable to criminals, because it can be used for scams and fake calls that sound very real.
What Is the ARTEX AI Tool?
The ARTEX AI tool is an open-source program built in China and shared on GitHub, mostly among Chinese-speaking users. It is a type of AI penetration testing tool.
Penetration testing, or “pen testing”, is when a security team hires someone to break into their own systems on purpose, so they can find and fix weak spots before real criminals do. Usually, this is slow and needs skilled people.
ARTEX tries to automate that. You give it a mission, and it uses large language models (the same kind of technology behind AI chatbots) and several “agents” that work together. It can gather information about a target, look for weaknesses, plan a path in, and test whether the weakness is real.
Here is the key point: the tool itself is not evil. Defenders can use the same kind of tool to test their own networks. The problem starts when the wrong person points it at someone else’s bank.
How Did the Attack Work? An Easy Example
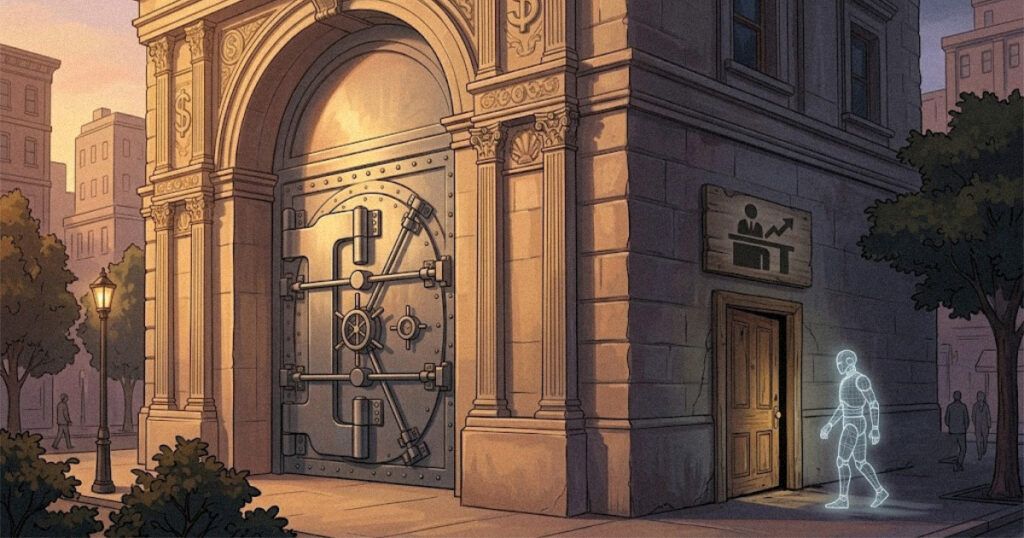
CrowdStrike says the attacker used ARTEX together with multiple AI models and old-school hacking methods. Media reports say the attackers went after less-watched doors, such as external websites and servers used by loan agents and staff for convenience, instead of the bank’s main vault.
Here is an imaginary example to make this easy to picture.
Meet Mina. She is a loan agent who works with a mid-sized bank. The bank gives her a web portal so she can check loan limits for customers while she is out meeting them. The main banking system is locked down tightly, but this little portal sits on the open internet.
An attacker points ARTEX at the bank and says, “Find a way in.” The tool does not get tired or bored. It maps out every public web page linked to the bank. It spots an old portal that has not been updated in a while. It tries a list of known weak points and common password tricks. It checks which attempts work, then plans what to try next.
A human hacker could do this too, but it might take days of boring, careful work. With AI, the tool does that repeat work while the hacker moves on to the next target. Now imagine the same hacker running this against five or six banks in the same week. That is what makes these AI-driven cyberattacks worrying: speed and scale.
Please note that Mina and her bank are made up. The point is how a small, forgotten side door can matter more than a strong front door.
How Did the Attacker Get Caught Out?
This is the most interesting part. The attacker left some server folders open to the public. CrowdStrike researchers found records of the attacker’s AI coding sessions, ARTEX settings files and AI “memory” files inside them.
That gave investigators a rare, direct look at how the operation was built and run. Reports say the attacker used several AI models, including DeepSeek, GLM and Grok, and that Chinese-language prompts were found. In one session, the attacker also asked an AI assistant where stolen Korean data is usually sold. That is one reason researchers think the motive is money.
In simple words: the attacker used smart tools but made a basic mistake by leaving the door to their own workshop open.
Why Agentic AI in Cybersecurity Changes the Game
You may have heard the word “agentic”. An agentic AI does not just answer a question. It takes a goal, makes a plan, performs steps, checks the result and tries again. That is a big shift from a simple chatbot.
Agentic AI in cybersecurity cuts both ways:
- For attackers: Less skill and less time are needed to run many break-in attempts at once.
- For defenders: The same helpers can scan their own systems around the clock, find weak spots early and respond faster to alerts.
CrowdStrike’s Adam Meyers put it this way: attackers are now mixing agentic AI tools with proven methods to move faster and work at a bigger scale. The key phrase is “proven methods”. Reports say the attacks were not brand new magic. They used well-known techniques. AI simply made them quicker and easier to repeat.
What We Do Not Know Yet
It is important to stay grounded. A few things are still unclear:
- Who is behind it? CrowdStrike has not tied the activity to any named group.
- How many victims are there? The full number is not yet known.
- How sure are the researchers? They say “moderate confidence” about the attacker’s language and motive. That is a careful way of saying “likely, but not certain”.
- Did one person do everything? Reports say many, but not all, of the hit companies are believed to be linked to the same attacker.
This story is still developing, so details may change as investigators learn more.
How to Protect Yourself From AI-Driven Cyberattacks
You do not need to be a bank to learn from this. Here are practical steps for everyday people and small businesses.
If you are a customer:
- Be extra careful with calls, texts and emails after any breach news. Scammers love to use real details to sound believable.
- Never share one-time codes, even if the caller knows your name and loan amount.
- Use a different strong password for each account, and turn on two-step login wherever you can.
If you run a business or manage a website:
List everything that faces the internet. Old test pages, partner portals and forgotten servers are the usual weak spots.
- Close what you do not need: If a page has no business purpose, take it offline.
- Use two-step login for staff and partners: A stolen password alone should never be enough.
- Limit failed logins and watch for strange patterns: Many attempts from odd places should raise an alarm.
- Keep software updated: Known weaknesses are the easiest ones to exploit.
- Test yourself first: Use an AI penetration testing tool or a trusted security partner to check your own systems before an attacker does.
Should Defenders Use AI Too?
Yes. South Korea’s regulators have already called for “defending against AI attacks with AI”. That makes sense. If attackers use machines to find weak spots in minutes, defenders cannot rely on yearly checks done by hand.
The sensible path is to use AI tools for the fast, repeat work, like scanning and sorting alerts, and keep trained humans in charge of the decisions. Any AI penetration testing tool should only be used on systems you own or have written permission to test.
Frequently Asked Questions
What is ARTEX?
ARTEX is an open-source, China-developed, AI-powered penetration testing tool. It uses large language models and multiple AI agents to automate the search for security weaknesses.
Who was behind the South Korean bank attacks?
Nobody has been named. CrowdStrike says the person is likely a Chinese-speaking, financially motivated actor, with moderate confidence.
Were customers’ bank accounts emptied?
Officials have said direct financial loss looks unlikely. The main risk is leaked personal data being used for scams.
Are AI-driven cyberattacks new?
Hackers have used automation for years. What is new is how well AI agents can plan and adjust their steps on their own, which makes attacks faster and cheaper.
How can I stay safe from AI-driven cyberattacks?
Use strong, unique passwords, turn on two-step login, stay alert to scam calls, and, if you run a business, shut down unused internet-facing systems.
The attacks on South Korean financial institutions are a clear sign of where cybercrime is heading. The methods were mostly familiar, but AI made them faster and easier to repeat. The good news is that the basics still work: know what you have online, lock it down, and keep watching.
AI-driven cyberattacks will keep growing, but so will the tools to fight them. The people who prepare early will be in the best position.